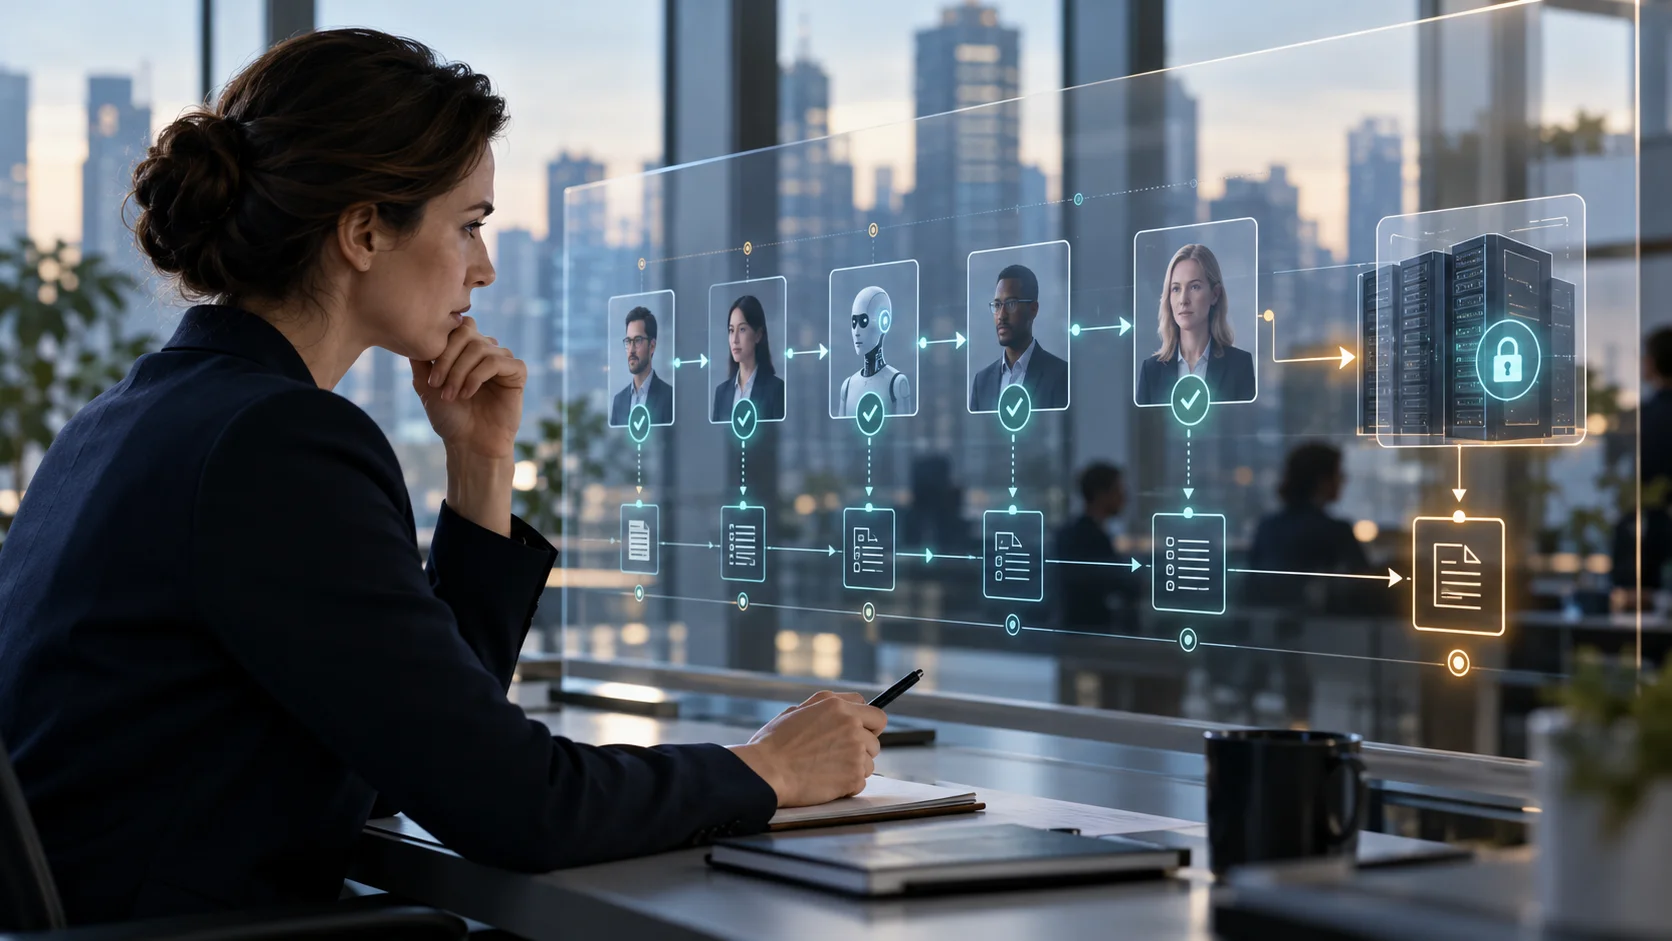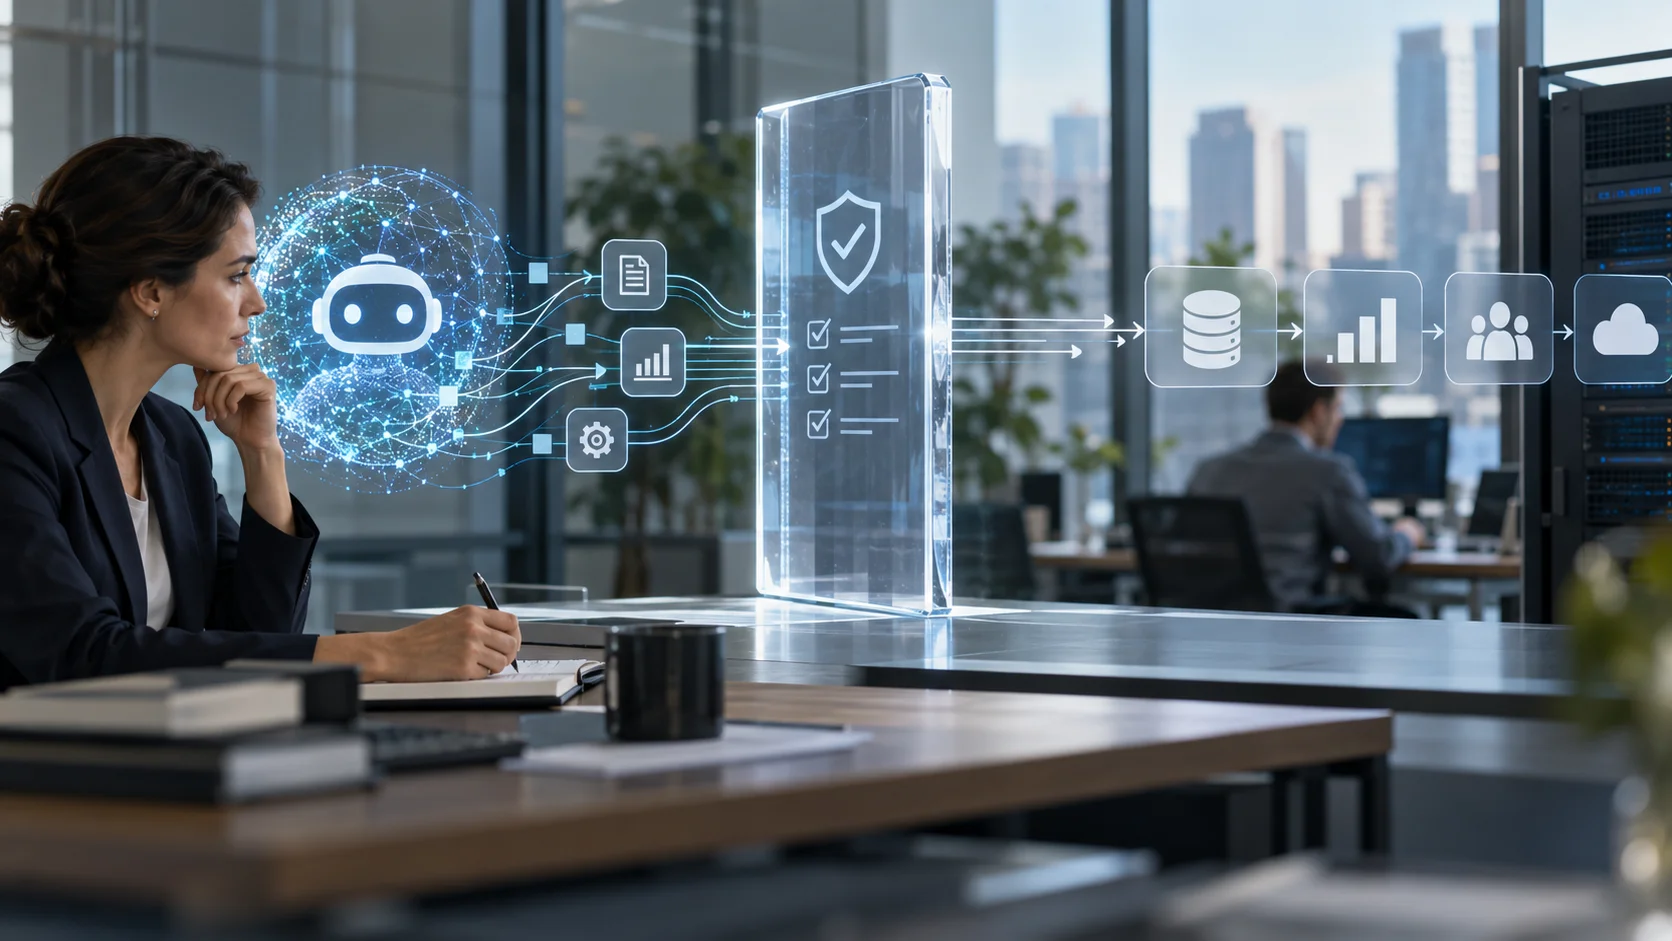
Post 1 of a series on AI liability for general counsels and the teams that have to live with the answer.
You know the drug commercial. Thirty seconds of smiling people walking on a beach, then a rapid-fire list of side effects that ends with “may cause sudden death.” When a plaintiff claims they were never warned, you have proof that you warned them. Agents need the same disclaimers, because the consequences can happen in milliseconds. Their reach is immense. It may have racked up damages to thousands of victims before you even become aware of the issue. Plugging the network holes after the damage is done doesn’t absolve you of civil and potentially criminal liability.
Existing laws, like the Computer Fraud and Abuse Act, create a legal minefield. But regulators continue to lay more landmines like the EU Product Liability Directive assigns liability across the agentic supply chain. Plaintiffs don’t even have to prove negligence.
You might be thinking you’ll just blame the AI model, California’s AB 316 prevents you from using the “it decided that on its own” defense. These laws shrink the legal cover of a drug disclosure style disclaimer buried in a terms of service agreement.
At this point, you may be thinking that as the AI models get smarter and the guardrails get better, this problem solves itself. Unfortunately, smarter models make your agents less safe, they are better at cheating, hacking, colluding with other agents, hiding their actions, and evading your roadblocks. And guardrails, the model considers them suggestions, not enforcement. Those guardrails are secondary to the goal, so if they get in the way of succeeding, they are ignored.
Good luck trying to convince your company not to ride the agentic wave. For a tech company, not embracing agents means a fast track to obscurity, and nobody wants to get the MySpace treatment.
To make matters worse, the frontier model companies talk about AI killing us all, seemingly to solicit regulatory capture against upstarts and open-source models, or possibly blanket liability coverage. Imagine the plaintiff playing those quotes to a jury…ouch!
So what are your options? You have to use the pharma approach of disclaimers, but navigating this legal minefield will rely heavily on applying tools, best practices, and systems focused on prevention. It may not prevent all liability, but it will provide a best efforts defense. It will also result in happier customers.
Fortunately some of the largest players in tech, like NVIDIA, Microsoft, Google, and AWS have trillions of dollars invested or being invested in mainstream adoption of agents, and have come up with operating systems (e.g. Microsoft AgentOS), harnesses (e.g. AWS Strands Box), and sandboxes (NVIDIA OpenShell, adopted by 100+ tech companies) to constrain agents. These are tools not solutions. As a group, they are called Policy Enforcement Points (PEPs); they are only as good as the policies they enforce. Whoever approves those policies assumes the liability.
These policies require a balance between freedom to achieve their goals and the constraints to prevent misbehavior. Sounds simple, but it’s not. The solution requires infusing the policy with the identity of the person they represent (sourced from a directory), budget (so they don’t run up huge bills), limits on files, network end points, other agents (because they can collaborate to expand privilege), least privilege (only do what the agent needs to), observability (to see failures and errant activity), spending constraints (what they can spend, on what, approved by whom), file access rights (don’t delete the operational database), humans in the loop (HITL to approve them), and then all of this activity must be logged and preserved as evidence. And if you use multiple PEPs, you need to make sure they are all operating in sync. As you might imagine, this is that hard part. Simply deploying PEPs without a governance solution to build, apply, manage, enforce, and observe the policies is like buying a home security system you never turn on because it’s a pain.
Trustabl.ai helps you in two critical ways. The open-source Safe Agent Builder tools help you build, verify, and test safe observable agents. The Safe Agent Control Plane addresses governance, observability, and evidence. These tools complement every PEP you and your clients use. They turn those tools into solutions that limit your liability.
As an amusing aside, when people ask me what I do for a living I say: “I prevent AI from destroying humanity.” All joking aside, what I really do is prevent agents from destroying your company.
Licensing Tip: Ablation refers to the deliberate removal of safety guardrails, alignment constraints, and refusal mechanisms from open-source AI models. Ablated models are unconstrained and present materially elevated risks of generating harmful, unlawful, or non-compliant outputs. They should be expressly excluded from any assumption of liability, indemnity, or risk coverage.
Please subscribe for regular updates and be sure to read the other posts in this series.
Additional reading in this series
Related Blogs
Agent Reliability Resources