Officers and directors must now sign off on cybersecurity risk under both USA and EU regulations. We believe that it is just a matter of time before the same applies to agentic risk.
Post 9 of a series on AI liability for general counsels interested in the legal liability associated with building and using agents.
The board packet used to include a cybersecurity update (regulations: USA, EU). Now it includes an agent update, or it should. An incident occurs. An agent exceeds its authority, leaks data, or generates a loss. The first question from the board, the insurer, or the plaintiff’s lawyer is not only what the agent did. It is what the directors knew, what they were shown, and whether they exercised oversight. Cybersecurity has already produced personal exposure for directors who failed to oversee risk. Agent risk is following the same path.
Most boards receive high-level assurances. Agents are “governed.” Policies exist. Vendors have been reviewed. When the question becomes specific (which agents are in production, who owns them, what they are allowed to do, what tools actively enforce the policies, what has already gone wrong, and whether the controls can be shown) the answers are scattered. The inventory lives in one spreadsheet. The policy lives in another system. The incident log lives in a third. The evidence that a given run stayed inside its ceilings does not exist in a form a director can review or a regulator can verify. An oversight duty that cannot be demonstrated is an oversight duty that has not been met.
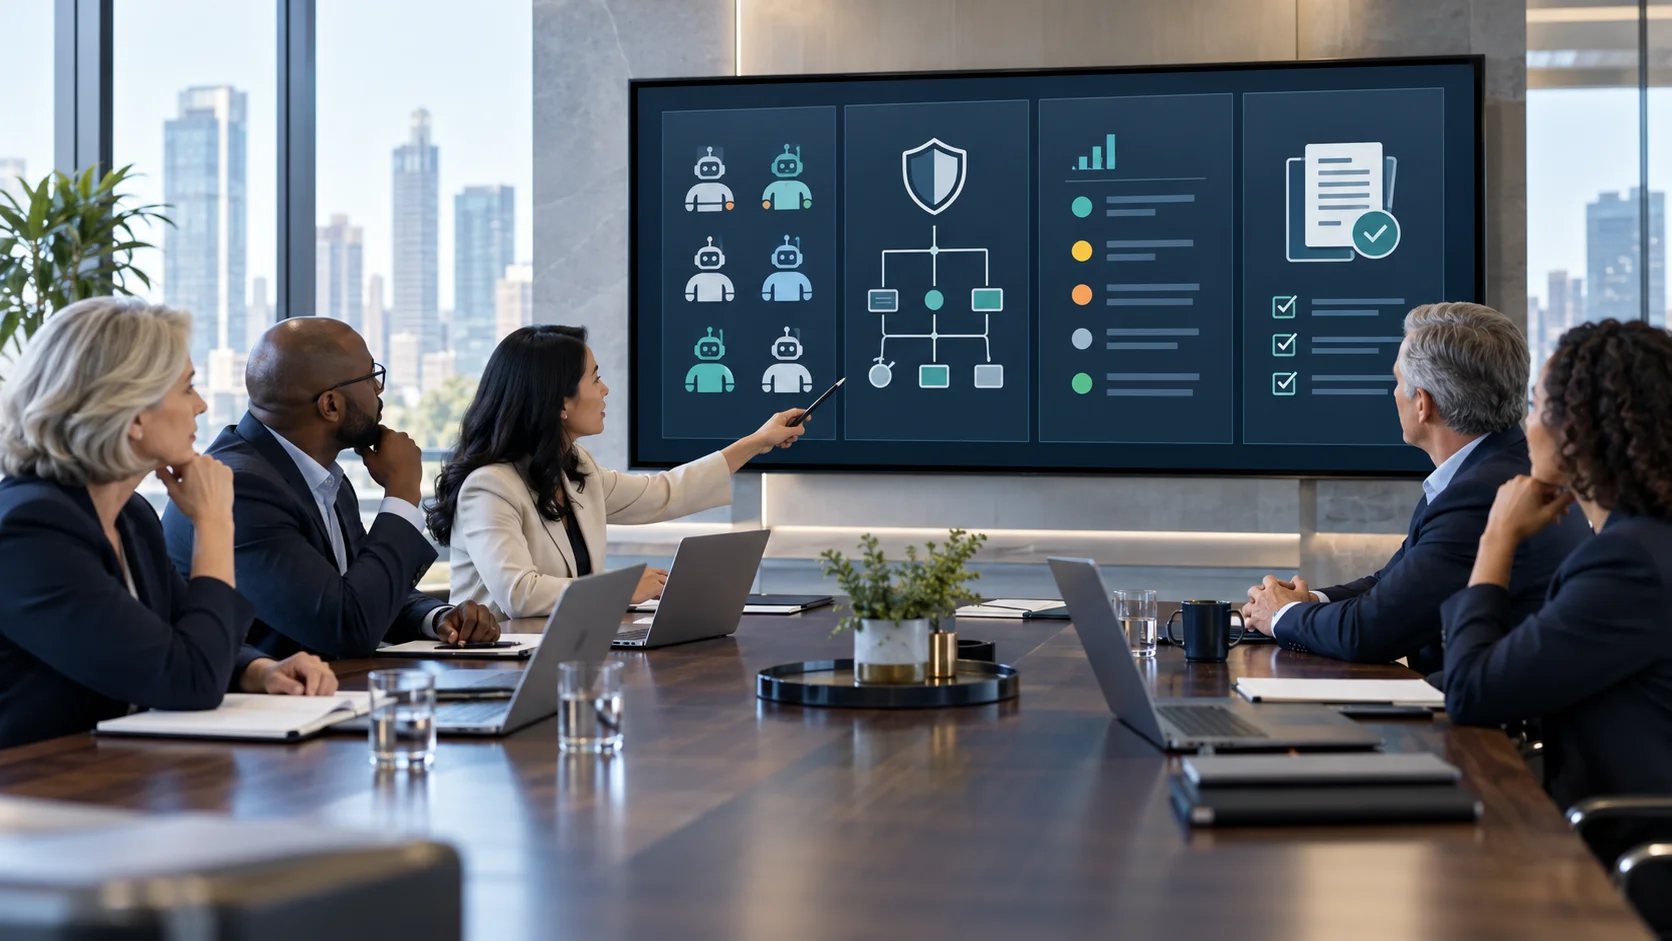
The emerging expectation is concrete. Boards are being told they should receive an inventory of production agents, the business function and risk classification of each, the identity of the executive sponsor, any incidents or near-misses, and evidence that controls are mapped and operating. The same package insurers request is the package directors need. A signed policy artifact, Analyzer or equivalent results showing must-fix items were resolved, and traces of actions and approvals give the board a record that oversight occurred. A narrative that oversight was intended does not.
The practical requirements are the ones already needed for the other liability vectors, surfaced for the board. You need a current inventory of production agents with clear ownership. You need published acceptance criteria (data classes, tools, budgets, handoff rules, human-approval points) that the organization has adopted. You need those criteria compiled into signed contracts the runtime enforces. You need incident and near-miss reporting that includes agent activity. You need the ability to export the signed artifact, the control mapping, and the corresponding traces so the board (and later an insurer or regulator) can see what was required and what occurred. You need that package on a recurring cadence, not only after something breaks.
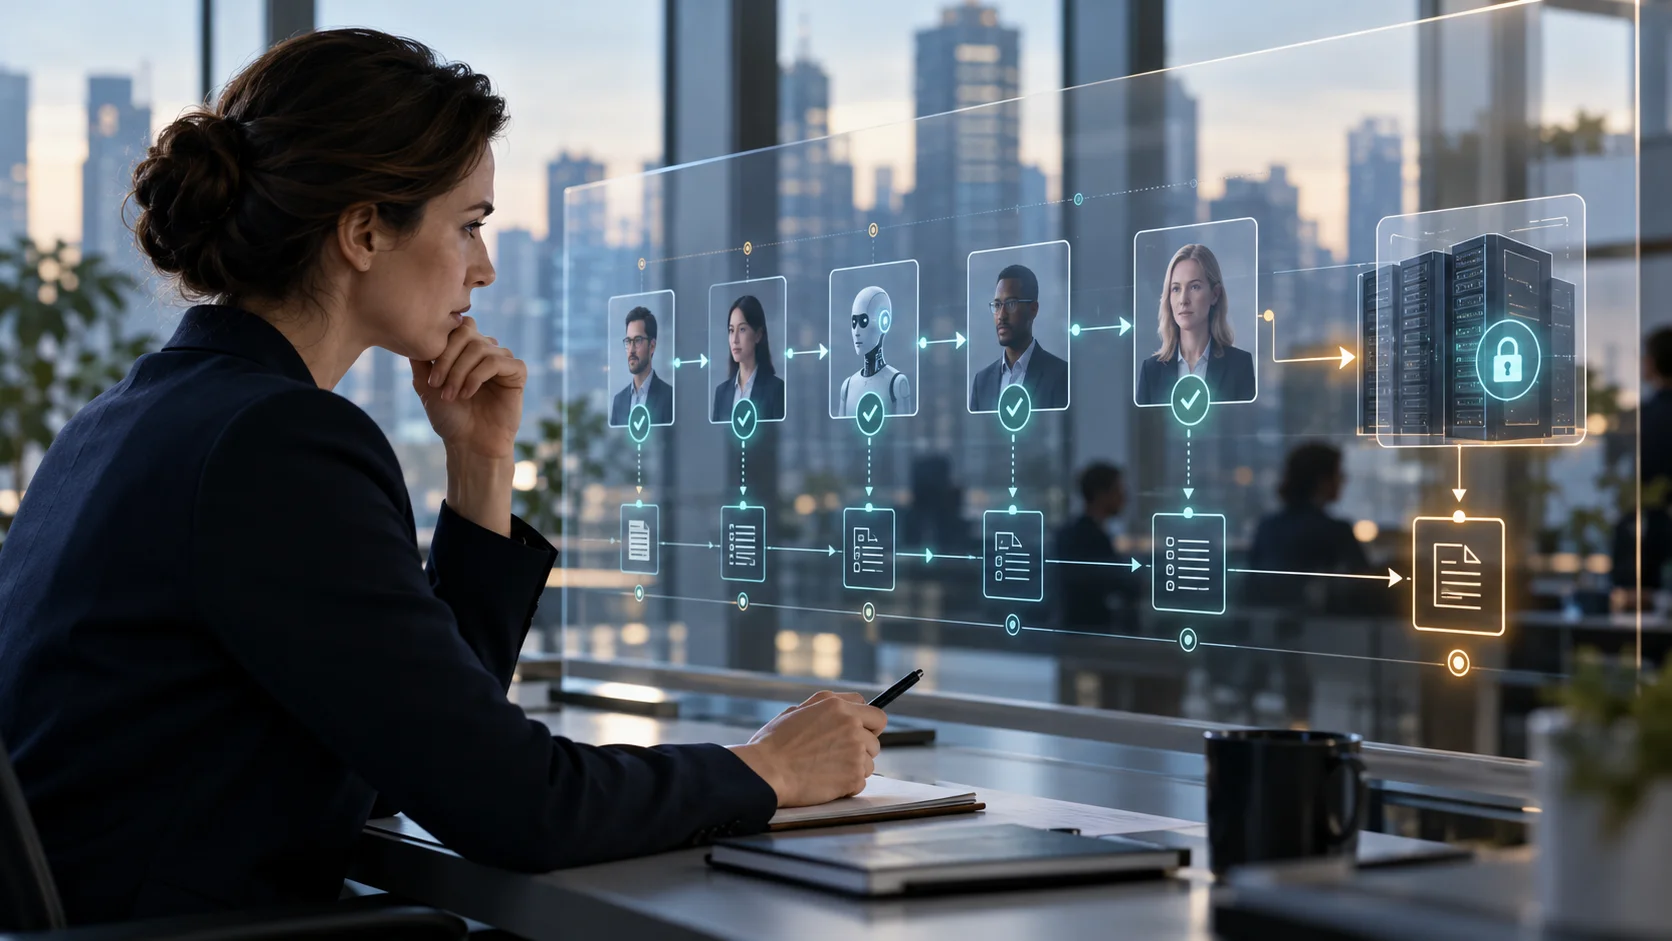
At Trustabl we treat the board evidence package as a direct output of the same controls that limit operational liability. Company Policy is the acceptance criteria the organization sets and the board can be shown. The compiler turns it into a single signed contract and generates the policies for the Policy Enforcement Points (PEPs). The Safe Agent Control Plane maintains the inventory linkage, the traces, and the evidence bundle a director or committee can review. The open-source Safe Agent Builder tools help teams produce agents that meet the safety criteria the board was told was already in place. We do not claim this eliminates director exposure. We claim it gives directors a verifiable record that they received the inventory, the controls, and the incidents, which is the difference between oversight and a statement that oversight was discussed.
Agents will keep creating events that reach the board. The companies whose directors can point to a signed policy, an inventory, and traces will be in a different position from the companies whose directors can only say they were told the agents were governed.
Additional reading in this series
Related Blogs
Agent Reliability Resources